Banner 468

pardon hackers
Facebook
RSS
Showing posts with label tools. Show all posts

back orifice trojan horse


 Back Orifice 2000 

BO2K or Back Orifice 2000 is one of the most POWERFULL trojans/admin tools out there well for the microsoft environment its not just a trojan , its also a remote network administration tool
so you can use it to hack and if ur an admin
it can make your life a bit eisier i belive if you can master this trojanyou can master any trojan this is realy only foradvanced users (as it was first made for linux) its default TCP port is18006 if its UDPIO the port will be 54320.

Make your server

Like SubSeven there is an edit server this is called bo2kcfg open it it willask you for ports and passwords just use thedefault port 18006 for TCP networking then it will go onto BO2K serverconfiguration select your server (BO2K) and insertthe BO_PEEP plugin this comes in the zip file adding this plugin will addthe vid streem option and hijack option BO_PEEPalso lets the server communicate better with the client then go to thestealth sub folder and enable the server to start upon the victims startup and you can change some default ports if you want butits not a good idia another good plugin to haveis Rattler v10 this send an email when the user is online but you need toconfigure this from the client. again re-namethe server and then get the IP from netstat -n now heres some thingdiffernet open bo2kgui this is the client then click thelittle computer in the bottom left it will come up with edit server settingsname of server well say you named the servermy pic put my pic in there the server address if there ip is http://www.facebook.com/l/165e3O03koA-Kq_cybr5mBOftCg/123.456.78.910and ur port is 18006 put in there http://www.facebook.com/l/165e3O03koA-Kq_cybr5mBOftCg/123.456.78.910:18006 then click ok then connect...it will say something like <BO2K BACK ORIFICE 1.0> in the server responcesection now this is pritty hard to master lets sayyou wanna log the victims key strokes you go to keylogging log keystrokesthen it will say diskfile this is where you wannalog the key strokes to type in a path likeC:\windows\system\catroot\{127D0A1D-4EF2-11D1-8608-00C04FC295EE} some wheretheywill never look then wait for around 20mins then go to stop keylogging andsend the command then to view keystroke logsC:\windows\system\catroot\{127D0A1D-4EF2-11D1-8608-00C04FC295EE} then sendcommand it will the let you view the logs in theserver responce section just mess around with it you will get it its one ofthose trojan that you need to work out your selftheres just so many commands for me to go frew them all but heres someoptionsKeyloggingM$ networkingTCP\IPnetwork mappingfile managerREGEIDTand more and belive me there is loads more also you can infect networks withthis trojan but its not a good idia becausean admin will spot it right away unless your an admin your self and want touse it to well admin things....:-)

[ Read More ]

trojan horse Guptachari

What is Guptachar ?
Guptachar is a remote administration tool ( trojan ) . This means that once you install Guptachar on computer A, you can control computer A from any computer B provided that both computer A and computer B are on the same IP based network like the Internet.
Guptachar also differs from most remote administration tools in one respect. It does not require its own client. This is because Guptachar runs as a web server. So once you've installed Guptachar on Computer A, all you need on Computer B is a web browser.
Guptachar has various features which allow you to administer the remote computer (aka Computer A) like browsing files, uploading files, executing programs, logging keys, shutting down and restarting, etc.

I've got Guptachar installed, how do I do the controlling ?
Say you've got Guptachar installed on Computer A whose IP address is 10.7.1.5, just point your web browser to http://10.7.1.5/ and enjoy.
If you've chosen to install Guptachar on a port other than 80 (discussed in the section on installation), say 8081, simply point your browser to http://10.7.1.5:8081/ instead.

How do I get to know the remote computer's IP Address ?
That's a good question. If computer A accesses the internet through dialup, it is likely to have a different IP address every time it logs on. This is why Guptachar has the facility of an IRCBOT.
Basically, if the IRCBOT feature is activated,whenever the remote computer (Computer A) goes online, Guptachar will connect to an IRC server with a predefined nickname, providing its IP address as its real name. So, whenever you want to know Computer A's IP address, you also connect to the same IRC server (use an IRC client like mIRC) and type /whois nickname.
While installing Guptachar (or by changing its server options), you can specify which IRC server and with what nick to logon. In case, the nickname you specify is already occupied, it'll try to logon with variations of the nick. Say, the nick you specified was gupt, it'll try to login as gupt, then gupt1, then gupt2, etc.
You can also ask Guptachar to connect to IRC via an HTTP proxy. Beware though, some IRC servers do not allow you to connect through a proxy (especially an open one).

How do I install Guptachar ?
Normal Installation
Just run the install.exe file. It'll ask you a series of questions and then install Guptachar on your machine.
Firstly, it'll ask you which port you want Guptachar to work on. Now webservers usually work on port 80. But it might not be such a good idea to operate on that port. Also, if you are installing it on an account with insufficient priveleges, you may be forced to use a higher port no. Remember this though, if you use a port other than 80, say 8081, you'll need to point your browser at http://ipaddress:8081/ instead of http://ipaddress/ or just ipaddress.
Then, it'll ask you whether you want access to the machine to be restricted and if so, it'll ask you for a username password pair.
Then it'll ask you whether you want Keylogging to be enabled. Following this, it'll ask you details about the IRCBOT feature.
Most of these options can be changed later through Guptachar, mostly using Server Options.
Making a Quick Installer
A quick installer is a stand alone .exe file, which has both the guptachar binaries as well as your inputted options stored within itself. Just running the .exe file will install Guptachar on the system without any user interaction. This quick installer will be considered as a virus by most of the antivirus to avoid detection use techinques like binding
To make a quick installer, just run makeqinst.exe. It'll first ask you for the filename of the quickinstaller (ie. the name of the .exe file) and then the same questions that it asks during normal installation.
Running makeqinst.exe does not install Guptachar on your system.
You'll need to run the generated .exe file to actually install Guptachar.

click here to download

[ Read More ]

send free anonymous email using online fake mailer


Email spoofing is email activity in which the sender address and other parts of the email header are altered to appear as though the email originated from a different source. Because core SMTP doesn't provide any authentication, it is easy to impersonate and forge emails.
Although there are legitimate uses, these techniques are also commonly used in spam and phishing emails to hide the origin of the email message.
By altering an email's identifying fields, such as the From, Return-Path and Reply-To (which can be found in the message header), email can be made to appear to be from someone other than the actual sender.[2]
Occasionally (especially if the spam requires a reply from the recipient, as in advance-fee frauds), the source of the spam email is indicated in the Reply-To field (or at least a way of identifying the spammer); if this is the case and the initial email is replied to, the delivery will be sent to the address specified in the Reply-To field, which could be the spammer's address. However, most spam emails (especially malicious ones with a trojan/virus payload, or those advertising a web site) forge this address too, and replying to it will annoy an innocent third party.
Prior to the advent of unsolicited commercial email (spam) as a viable business model, "legitimately spoofed" email was common. For example, a visiting user might use the local organization's SMTP server to send email from the user's foreign address. Since most servers were configured as open relays, this was a common practice. As spam email became an annoying problem, most of these "legitimate" uses fell victim to antispam techniques.
It is much more difficult to spoof or hide the IP or Internet Protocol address. The IP address is a 32 or 128 bit numerical label assigned to each device participating in a network and originates through the network provider making it more difficult to spoof or hide. Although this kind of verification is difficult for individual users, companies can use this technology as well as others such as cryptographic signatures (e.g., PGP "Pretty Good Privacy" or other encryption technologies) to exchange authenticated email messages. Authenticated email provides a mechanism for ensuring that messages are from whom they appear to be, as well as ensuring that the message has not been altered in transit. Similarly, sites may wish to consider enabling SSL/TLS in their mail transfer software. Using certificates in this manner increases the amount of authentication performed when sending mail.

CLICK HERE to go to online fake mailer tool

[ Read More ]

Email tracking(ip)

Hai this post is for noobs if you are a daemon ignore it!!!
Tracing mails you recieve
                    If you have any abusive mails or if you want to trace victims IP address or if you want to know whether your friend has read your mail then this will help you
Here it goes:
                    You can trace the email received by analyzing the header actually this could be done manually ,but i wont be recommending that becoz there are tools which make life easier follow the steps
1.open the email header (you can find the header by clicking show original option in gmail)
2.copy the header and paste in below mentioned tools
Recommended tools:
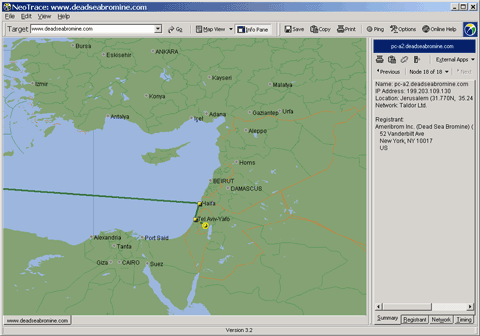
Utility name: Neo Trace Pro
Fantastic tool top recommended this will geographically trace your ip address .It is very accurate and has extremely useful functionalities.
Download from here
utility name: VisualRoute , Download from here
utility name: eMailTrackerPro , Download from here
Tracing the mails that you send
                Most of you find fun in this bcoz the tool i'm gonna explain will send you information when the victim opens it.All you need to do is visit spypig.com enter the required fields then it will give you a image which has to be sent to your victim. the tool looks like this
Step 1: Specify the email id to which you want to get the Destination's ip
Step 2: Here goes your message title
Step 3: Select the image you want to send , you may upload your own image too but its recommended to select the first one(white) becoz it will mix up with white background of your mail body so some one looking at this will think that there is no image
Step 4: Press the create button 
Step 5:Here the tricky part comes copy your image into your mail body within in the time limit shown by spy pig or else it will expire
Note : Use the New gmail version bcoz in older one you cant copy a image into body
Step 6: this step says you to send the mail

                    Hopefully if the victim opens the mail you will receive all the information of victim like OS,browser,ip & mac address
Note : there is no counter measure for this
HAPPY HACKING ;]
[ Read More ]